Overview
LILIN are dedicated to protecting our customers against cyber security attacks on our network cameras, network video recorders & VMS products. LILIN regularly review, investigate, report, and implement against cyber security vulnerabilities in our products.
LILIN's cyber security assurance team has been formed to manage cyber security threats throughout the lifecycle of its products; including design, development, verification, manufacturing and service phases. LILIN are constantly reviewing and enhancing our cyber security efforts to provide our valued customers with the highest quality, safe and reliable products.
LILIN cannot protect standardized network protocols and services from cyber-attacks, however we are committed to help minimize and prevent such events from occurring on LILIN products within our customers networks.
For the latest LILIN software and firmware updates, please visit this firmware download site. The latest firmware fixes or software patches are maintained at the site.
Vulnerability Management
LILIN are always working on maintaining the highest level of security for our products and customers. LILIN conducts product security maintenance throughout the product's life cycle. In short, the vulnerability management is described below:
- Risk analysis and assessment of vulnerabilities with reference to the CVSS 3.0
- Security guidance throughout development by CIA-AAA (confidentiality, integrity, availability, authentication, authorization & accounting)
- Secure programming guidance and FIPS 140-2 for sensitive data protection & cryptography
- Vulnerability and open ports scanning in the testing phase
- Third-party vulnerability auditing for LILIN products by our security partner Deloitte Taiwan
- Security controls and checkpoints for software/firmware releasing, loading and storing
Based on the risks reported and discovered, we classify the severity of vulnerabilities as either critical or non-critical. The process for identifying a security vulnerability is discover, analyze, prioritize, remediate & track.
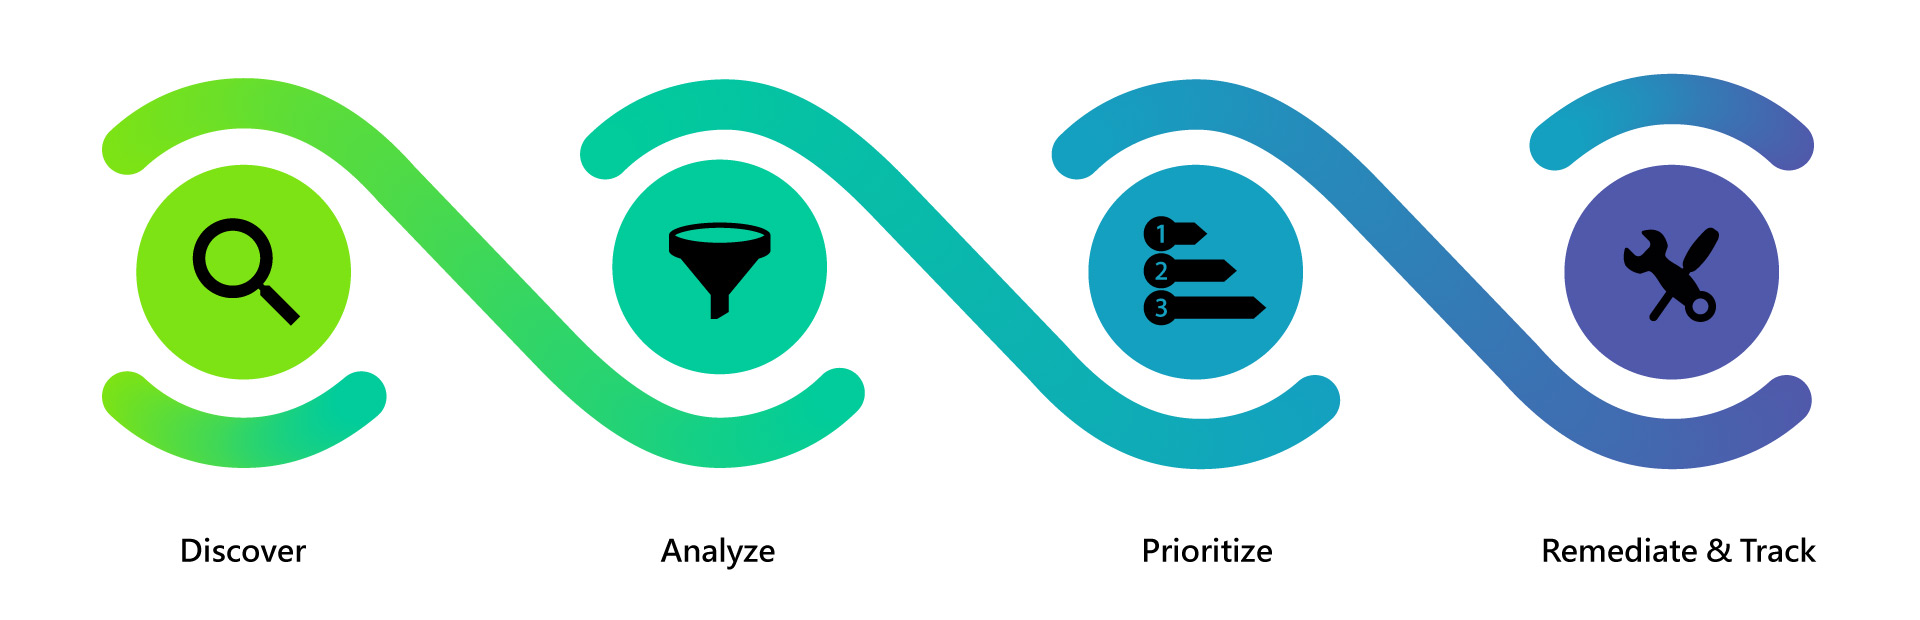
LILIN release firmware updates on a regular basis to address bug fixes and non-critical vulnerabilities that are found in our products. Occasionally, there may be a critical vulnerability discovered that leaves our devices vulnerable to attack. LILIN will focus its priorities to fix this issue immediately outside of the regular schedule and release a firmware fix for the vulnerable device.
Reporting Suspected Security Vulnerabilities
We encourage and welcome you report any cyber security vulnerabilities found in LILIN products to help us to resolve & eliminate these threats. Please contact us at [email protected] or raise a ticket at lilin.zendesk.com to report a vulnerability or other security concern.
LILIN will disclose and notify customers of any vulnerability found and of the resolution at LILIN Security Bulletins.
Response Process
LILIN has established the Product Security Incident Response Team (PSIRT) committee to analyze all submissions of vulnerabilities to [email protected] or lilin.zendesk.com. LILIN PSIRT uses version 3.0 of the Common Vulnerability Scoring System (CVSS) as part of its standard process of evaluating reported potential vulnerabilities in LILIN products.
LILIN PSIRT will endeavor to reply within 72 hours & if needed, will ask questions to help in identifying a solution.
Receiving Information from LILIN
LILIN have published this policy on LILIN Vulnerability Policy. Subscribe to our product news and updates via the LILIN web site.
We also encourage users to take advantage of our many online resources:
- Subscribe to LILIN news.
- LILIN Downloads: With useful materials, such as brochures, firmware/software updates.
- LILIN Support: Report any support issue via https://lilin.zendesk.com.
Security Third-Parties
LILIN strive to provide our customers with the highest level of product security. To do so, LILIN have partnered with Deloitte Taiwan and Electronics Testing Center, Taiwan, for product vulnerability auditing and checking. LILIN are also partnered with TAICS for the latest network product security standards.
LILIN Security Bulletins
LILIN constantly discloses and notifies customers of any vulnerability found with these bulletins.
No threat from the security vulnerability of Log4j for all LILIN products
Download the security solution
DHD DVR vulnerability found (immediate actions needed)
Download the security solution or review customers' letter here
CVSS 9.0 VULNERABILITY FOUND AT NVR FIRMWARE BY UPGRADING LIBUPNP TO 1.6.21.
Download the security solution